Off the Books and Into the Open: How Developers Built a Shadow Infrastructure for Reporting What Companies Refuse to Fix
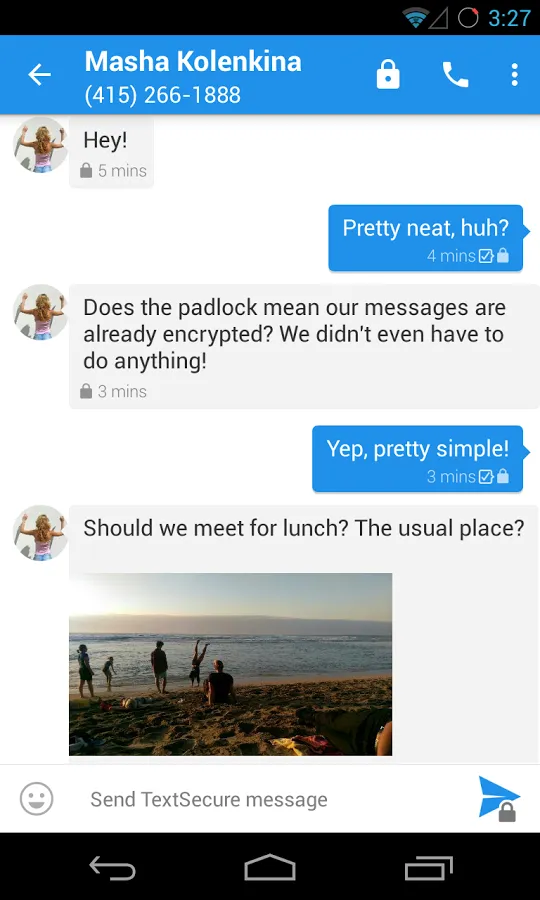
Photo: Open WhisperSystems, GPLv3, via Wikimedia Commons
Every major tech company has a process for reporting security vulnerabilities. Most of them also have a process for making those reports disappear.
A ticket is opened. A priority level is assigned. A comment is added six weeks later noting that the issue has been reviewed and determined to be "within acceptable risk tolerance." The ticket is closed. The developer who filed it has learned something about what their employer means when it says it takes security seriously.
What happens next — what a developer does when the official channel has failed and the unofficial channels carry real professional risk — is the subject of this guide. Across the United States, a loose but functional infrastructure has emerged for exactly this situation. It is worth understanding how it works, who built it, and what it actually costs to use it.
The Landscape of Informal Reporting
The channels developers use when internal processes fail exist on a spectrum from semi-public to genuinely anonymous, and from low-consequence to career-defining.
At the more accessible end of that spectrum sit communities like certain subreddits, Hacker News threads, and Discord servers oriented around security research. These spaces are not anonymous — they are pseudonymous at best — but they serve an important function as early amplifiers. A developer who posts a technically detailed account of an unaddressed vulnerability, even without naming the company, can attract the attention of independent security researchers, journalists, and regulators who know how to follow a thread.
Further along the spectrum are dedicated vulnerability disclosure platforms. HackerOne and Bugcrowd operate formal bug bounty programs on behalf of participating companies, but both platforms also maintain mechanisms for disclosing vulnerabilities in organizations that have not opted into a formal program. The Cybersecurity and Infrastructure Security Agency (CISA) operates its own coordinated vulnerability disclosure process and will engage with reports involving critical infrastructure regardless of whether the affected organization is cooperative.
At the far end of the spectrum are the tools and practices that security professionals associate with operational security: SecureDrop installations maintained by major investigative newsrooms, end-to-end encrypted communication via Signal with disappearing messages enabled, Tor-routed submissions to journalist contact forms, and air-gapped devices used exclusively for sensitive communications.
Case Studies: When Grassroots Disclosure Changed the Industry
The history of meaningful security disclosure is, in large part, a history of developers going outside official channels.
The coordinated disclosure of the Heartbleed vulnerability in 2014 involved a small number of researchers who worked outside any single company's internal process precisely because the affected library — OpenSSL — was maintained by a volunteer community rather than a corporate entity. The disclosure was carefully managed, but it was fundamentally a grassroots effort that compelled an industry-wide response.
More recently, the circumstances surrounding several high-profile cloud misconfigurations have involved independent security researchers — some of them current or former employees of affected companies — who published their findings after private notifications went unacknowledged. In a number of those cases, public disclosure was the only mechanism that produced a patch.
The pattern is consistent: when internal escalation fails, external visibility is often the only remaining lever. The question is how to apply that lever without destroying the hand holding it.
Operational Security for the Developer Who Needs It
If you are considering reporting outside official channels, the first thing to understand is that the threat model for a software developer is different from the threat model for a national security whistleblower — but it is not trivial.
Your employer has access to your work devices, your corporate email, and in many cases your Slack and Teams message history. If you have communicated about a vulnerability using company infrastructure, assume that record exists and may be reviewed. This is not hypothetical: several developers who have faced retaliation after external disclosures have described situations in which their internal communications were used to identify them as the source of a leak.
Before you communicate anything externally:
- Use a device your employer does not own or manage. A personal laptop on a home network, not a corporate machine on a VPN, is the baseline.
- Create a new email address through a privacy-respecting provider — Proton Mail is a reasonable choice for most threat levels — that is not linked to your real identity.
- If you are contacting a journalist, prioritize newsrooms that maintain SecureDrop instances. The New York Times, The Washington Post, and The Guardian all operate them. Instructions are available on each outlet's website.
- Signal is appropriate for direct journalist communication once initial contact has been established through a more anonymous channel. Enable disappearing messages.
- Do not discuss your intentions with colleagues using work tools, and be cautious about discussing them with colleagues at all until you have a clear sense of who can be trusted.
Document before you disclose. The most valuable thing you can bring to a journalist, a regulator, or a coordinated disclosure platform is specificity. Dates, ticket numbers, the names of people who received your reports, the language used in responses — all of it matters. Store documentation securely, off company infrastructure, before you need it.
The Real Consequences: What Developers Have Actually Faced
Operational security reduces risk. It does not eliminate it.
Developers who have engaged in external disclosure — even when they took significant precautions — have faced outcomes ranging from hostile reference calls to employment termination to civil litigation. Several have described the experience of being identified through circumstantial evidence: they were the only person at the company with access to a specific system, or the only one who had raised the relevant concern internally.
The legal landscape offers some protection. The Computer Fraud and Abuse Act, despite its history of misuse against security researchers, has been interpreted more narrowly in recent years following the Supreme Court's 2021 decision in Van Buren v. United States. Several states have enacted additional protections for security researchers acting in good faith. The SEC's whistleblower program offers financial awards and anti-retaliation protections for disclosures involving publicly traded companies.
None of these protections are automatic. Most require that you consult with an attorney — ideally one specializing in employment or whistleblower law — before taking action, not after.
The Ethics of Going Outside
The developers who maintain and use these informal networks are not, by and large, motivated by disruption. The ones who spoke with WhistleDev described a consistent set of priorities: they wanted the vulnerability fixed, they wanted users protected, and they had exhausted the internal options available to them.
That framing matters. Responsible disclosure — the practice of notifying an organization before going public, and giving it a reasonable window to respond — remains the ethical and legal standard for a reason. Going outside official channels is not a first step. It is what the absence of functional official channels sometimes makes necessary.
The infrastructure for doing it exists because the need for it exists. Understanding how to use it carefully is not an invitation to recklessness. It is recognition that the developers who hold the most important knowledge about a system's vulnerabilities deserve tools that are equal to the risks they are being asked to take.